

Unique Top-selling SY0-601 Exams - New 2024 CompTIA Pratice Exam
CompTIA Security+ Dumps SY0-601 Exam for Full Questions - Exam Study Guide
The CompTIA SY0-601 test is the exam that candidates must pass in case they want to acquire the core knowledge of the cybersecurity domain to perform fundamental security functions.
The CompTIA SY0-601 exam tests the candidates on a range of topics, including network security, threats and vulnerabilities, access control and identity management, cryptography, and risk management. SY0-601 exam is designed to validate the candidate's knowledge of the latest cybersecurity trends and best practices. CompTIA Security+ Exam certification is ideal for individuals who are interested in pursuing a career in cybersecurity or for professionals who want to validate their knowledge and skills in this field.
NEW QUESTION # 63
An organization has various applications that contain sensitive data hosted in the cloud. The company's leaders are concerned about lateral movement across applications of different trust levels. Which of the following solutions should the organization implement to address the concern?
- A. CASB
- B. UTM
- C. SWG
- D. ISFW
Answer: A
Explanation:
Once the full extent of cloud usage is revealed, the CASB then determines the risk level associated with each by determining what the application is, what sort of data is within the app, and how it is being shared. https://www.mcafee.com/enterprise/en-au/security-awareness/cloud/what-is-a-casb.html
A cloud access security broker (CASB) (sometimes pronounced cas-bee) is on-premises or cloud based software that sits between cloud service users and cloud applications, and monitors all activity and enforces security policies.[1] A CASB can offer a variety of services such as monitoring user activity, warning administrators about potentially hazardous actions, enforcing security policy compliance, and automatically preventing malware. https://en.wikipedia.org/wiki/Cloud_access_security_broker
NEW QUESTION # 64
A user reports constant lag and performance issues with the wireless network when working at a local coffee shop. A security analyst walks the user through an installation of Wireshark and get a five-minute pcap to analyze. The analyst observes the following output: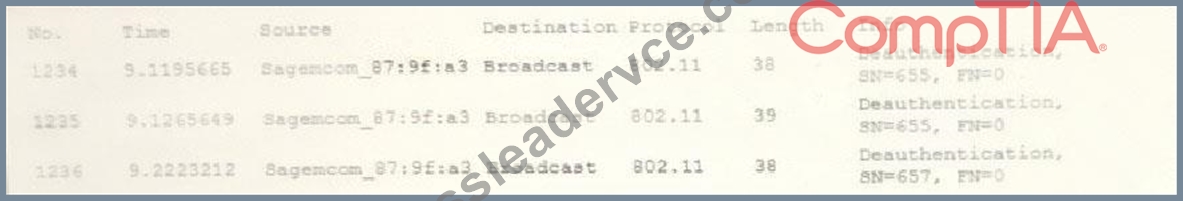
Which of the following attacks does the analyst MOST likely see in this packet capture?
- A. Session replay
- B. Bluejacking
- C. Evil twin
- D. ARP poisoning
Answer: C
NEW QUESTION # 65
A security analyst is running a vulnerability scan to check for missing patches during a suspected security rodent During which of the following phases of the response process is this activity MOST likely occurring?
- A. Preparation
- B. Recovery
- C. Identification
- D. Containment
Answer: C
Explanation:
Vulnerability scanning is a proactive security measure used to identify vulnerabilities in the network and systems. Reference: CompTIA Security+ Study Guide 601, Chapter 4
NEW QUESTION # 66
An employee's company account was used in a data breach Interviews with the employee revealed:
* The employee was able to avoid changing passwords by using a previous password again.
* The account was accessed from a hostile, foreign nation, but the employee has never traveled to any other countries.
Which of the following can be implemented to prevent these issues from reoccuring? (Select TWO)
- A. Geofencing
- B. Password lockout
- C. Geographic dispersal
- D. Password complexity
- E. Password history
- F. Geotagging
Answer: A,E
Explanation:
Explanation
two possible solutions that can be implemented to prevent these issues from reoccurring are password history and geofencing12. Password history is a feature that prevents users from reusing their previous passwords1. This can enhance password security by forcing users to create new and unique passwords periodically1. Password history can be configured by setting a policy that specifies how many previous passwords are remembered and how often users must change their passwords Geofencing is a feature that restricts access to a system or network based on the geographic location of the user or device2. This can enhance security by preventing unauthorized access from hostile or foreign regions2
. Geofencing can be implemented by using GPS, IP address, or other methods to determine the location of the user or device and compare it with a predefined set of boundaries
NEW QUESTION # 67
After a phishing scam for a user's credentials, the red team was able to craft a payload to deploy on a server. The attack allowed the installation of malicious software that initiates a new remote session.
Which of the following types of attacks has occurred?
- A. Session replay
- B. Privilege escalation
- C. Application programming interface
- D. Directory traversal
Answer: B
NEW QUESTION # 68
Phishing and spear-phishing attacks have been occurring more frequently against a company's staff. Which of the following would MOST likely help mitigate this issue?
- A. The addition of DNS conditional forwarders
- B. DNSSEC and DMARC
- C. Exact mail exchanger records in the DNS
- D. DNS query logging
Answer: C
NEW QUESTION # 69
The primary goal of the threat-hunting team at a large company is to identify cyberthreats that the SOC has not detected. Which of the following types of data would the threat-hunting team primarily use to identify systems that are exploitable?
- A. Vulnerability scan
- B. Threat feed
- C. Packet capture
- D. User behavior
Answer: A
Explanation:
Explanation
A vulnerability scan is a type of data that can identify systems that are exploitable by detecting known weaknesses and misconfigurations in the software and hardware. Packet capture, threat feed, and user behavior are types of data that can help identify malicious activities or indicators of compromise, but not necessarily the systems that are vulnerable to exploitation.
NEW QUESTION # 70
Which of the following would MOST likely be identified by a credentialed scan but would be missed by an uncredentialed scan?
- A. Vulnerabilities with a CVSS score greater than 6.9.
- B. Missing patches for third-party software on Windows workstations and servers.
- C. CVEs related to non-Microsoft systems such as printers and switches.
- D. Critical infrastructure vulnerabilities on non-IP protocols.
Answer: B
Explanation:
Explanation
An uncredentialed scan would miss missing patches for third-party software on Windows workstations and servers. A credentialed scan, however, can scan the registry and file system to determine the patch level of third-party applications. References: CompTIA Security+ Study Guide by Emmett Dulaney, Chapter 4:
Identity and Access Management, The Importance of Credentialing Scans
NEW QUESTION # 71
A company recently experienced an attack during which its main website was directed to the attacker's web server, allowing the attacker to harvest credentials from unsuspecting customers.
Which of the following should the company implement to prevent this type of attack occurring in the future?
- A. IPSec
- B. S/MIME
- C. DNSSEC
- D. SSL/TLS
Answer: C
NEW QUESTION # 72
An amusement park is implementing a btomelnc system that validates customers' fingerpnnts to ensure they are not sharing tickets The park's owner values customers above all and would prefer customers' convenience over security For this reason which of the following features should the security team prioritize FIRST?
- A. Low CER
- B. Low efficacy
- C. Low FRR
- D. Low FAR
Answer: C
Explanation:
FAR (False Acceptance Rate)
FRR (False Rejection Rate)
CER (Crossover Error Rate) AKA ERR (Equal Error Rate)
since he is willing to sacrifice Security for Customer Service, Best way to understand this is.
FAR has to go up in order for FRR to go down.
typical business practice is in the middle of both which would be near the CER.
NEW QUESTION # 73
A security administrator is working to secure company data on corporate laptops in case the laptops are stolen.
Which of the following solutions should the administrator consider?
- A. Disk encryption
- B. Data loss prevention
- C. Boot security
- D. Operating system hardening
Answer: A
NEW QUESTION # 74
Which of the following uses six initial steps that provide basic control over system security by including hardware and software inventory, vulnerability management, and continuous monitoring to minimize risk in all network environments?
- A. NIST Risk Management Framework
- B. ISO 27701
- C. SSAE SOC 2
- D. The Center for Internet Security
Answer: D
Explanation:
Explanation
The Center for Internet Security (CIS) uses six initial steps that provide basic control over system security, including hardware and software inventory, vulnerability management, and continuous monitoring to minimize risk in all network environments. References:
* CompTIA Security+ Certification Exam Objectives 1.1: Compare and contrast different types of security concepts.
* CompTIA Security+ Study Guide, Sixth Edition, pages 15-16
NEW QUESTION # 75
An enterprise needs to keep cryptographic keys in a safe manner. Which of the following network appliances can achieve this goal?
- A. HSM
- B. TPM
- C. DLP
- D. CASB
Answer: A
Explanation:
Explanation
Hardware Security Module (HSM) is a network appliance designed to securely store cryptographic keys and perform cryptographic operations. HSMs provide a secure environment for key management and can be used to keep cryptographic keys safe from theft, loss, or unauthorized access. Therefore, an enterprise can achieve the goal of keeping cryptographic keys in a safe manner by using an HSM appliance. References: CompTIA Security+ Certification Exam Objectives, Exam Domain 2.0: Technologies and Tools, 2.4 Given a scenario, use appropriate tools and techniques to troubleshoot security issues, p. 21
NEW QUESTION # 76
Given the following logs: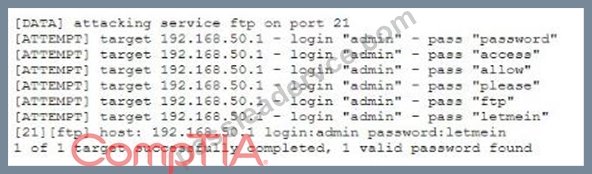
Which of the following BEST describes the type of attack that is occurring?
- A. Dictionary
- B. Password spraying
- C. Rainbow table
- D. Pass-the-hash
Answer: B
NEW QUESTION # 77
A company is setting up a web server on the Internet that will utilize both encrypted and unencrypted web-browsing protocols. A security engineer runs a port scan against the server from the Internet and sees the following output: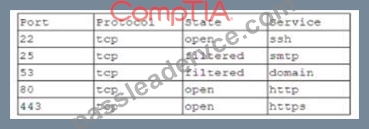
Which of the following steps would be best for the security engineer to take NEXT?
- A. Block SSH access from the Internet.
- B. Allow DNS access from the internet.
- C. Block HTTPS access from the Internet
- D. Block SMTP access from the Internet
Answer: A
NEW QUESTION # 78
Which of the following would BEST identify and remediate a data-loss event in an enterprise using third-party, web-based services and file-sharing platforms?
- A. CASB
- B. UTM
- C. DLP
- D. SIEM
Answer: A
Explanation:
Microsoft has a straightforward definition and it includes DLP. "is a security policy enforcement point positioned between enterprise users and cloud service providers" https://www.microsoft.com/en-us/security/business/security-101/what-is-a-cloud-access-security-broker-casb A cloud access security broker (CASB) works by securing data flowing to and from in-house IT architectures and cloud vendor environments using an organization's security policies. CASBs protect enterprise systems against cyberattacks through malware prevention and provide data security through encryption, making data streams unreadable to outside parties. CASBs were created with one thing in mind: protecting proprietary data stored in external, third-party media. CASBs deliver capabilities not generally available in traditional controls such as secure web gateways (SWGs) and enterprise firewalls. CASBs provide policy and governance concurrently across multiple cloud services and provide granular visibility into and control over user activities. https://www.forcepoint.com/cyber-edu/casb-cloud-access-security-broker
NEW QUESTION # 79
......
The SY0-601 exam consists of 90 questions, which are multiple-choice and performance-based. SY0-601 exam is designed to test the candidate's knowledge and skills in identifying and mitigating security threats, implementing secure network designs, and managing access control. SY0-601 exam is also designed to test the candidate's knowledge of the latest security technologies, such as cloud security, mobile device security, and virtualization security.
Best way to practice test for CompTIA SY0-601: https://www.passleadervce.com/CompTIA-Security/reliable-SY0-601-exam-learning-guide.html
SY0-601 Dump Ready - Exam Questions and Answers: https://drive.google.com/open?id=1HRfeavUfAjnEG9K5_HwZahEncnN_fQ4y